Our product · In development
KyAuth
A two-factor authenticator that makes no network calls at all.
- Network calls, of any kind
- 0
- TOTP, plus HOTP under RFC 4226
- RFC 6238
- App lock with auto-lock
- Biometric
- Colour, shown only when a secret is exposed
- 1
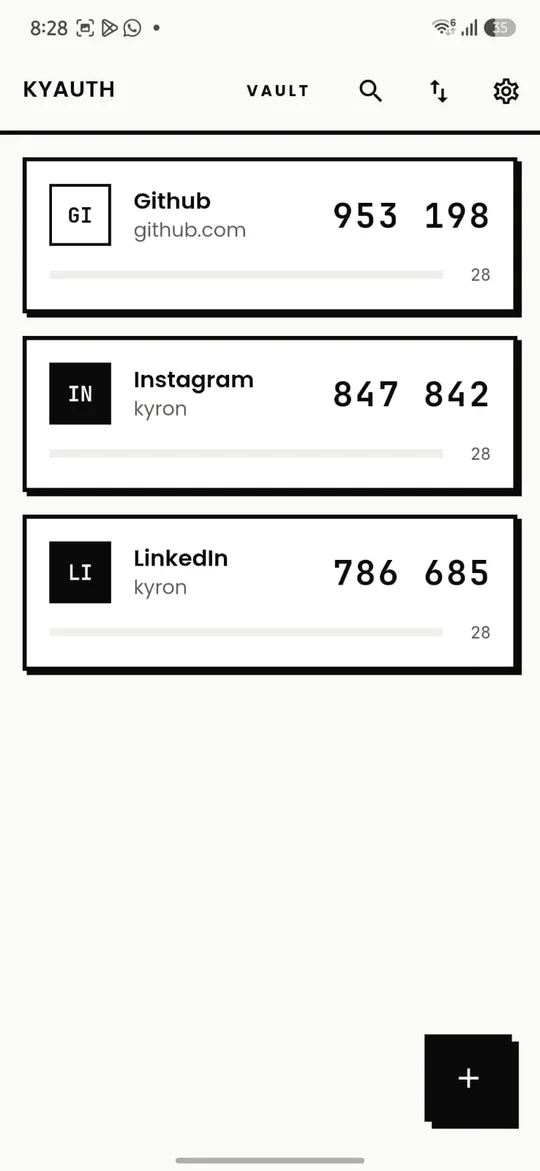
Codes
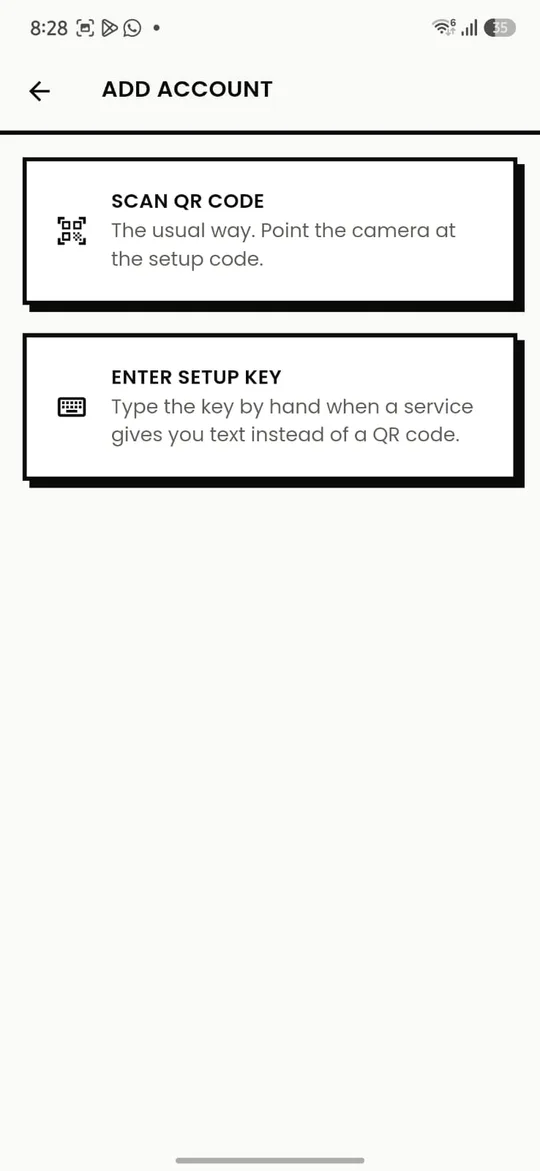
Add an account
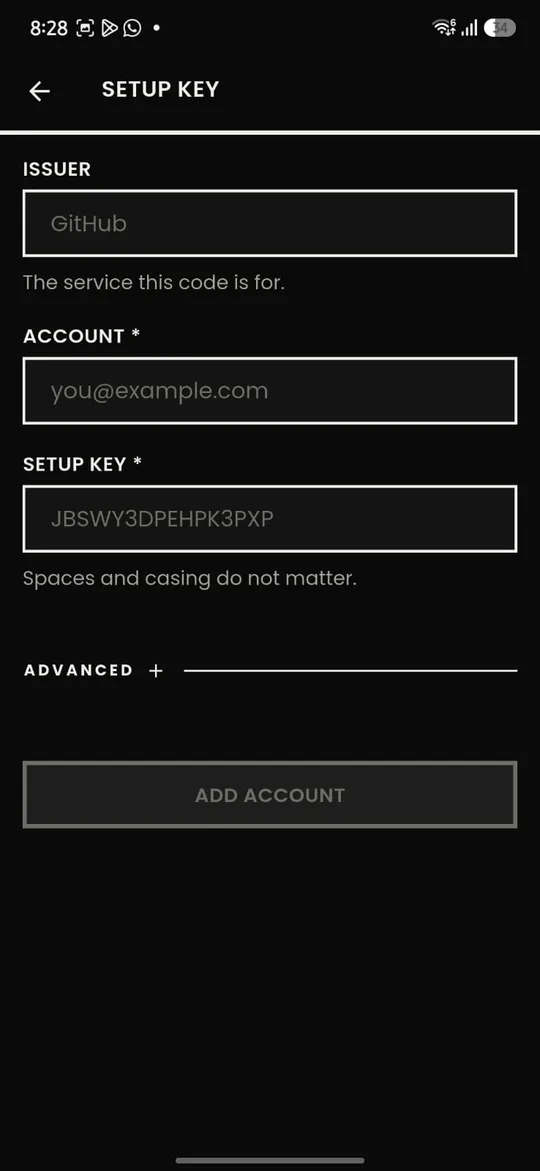
Setup key
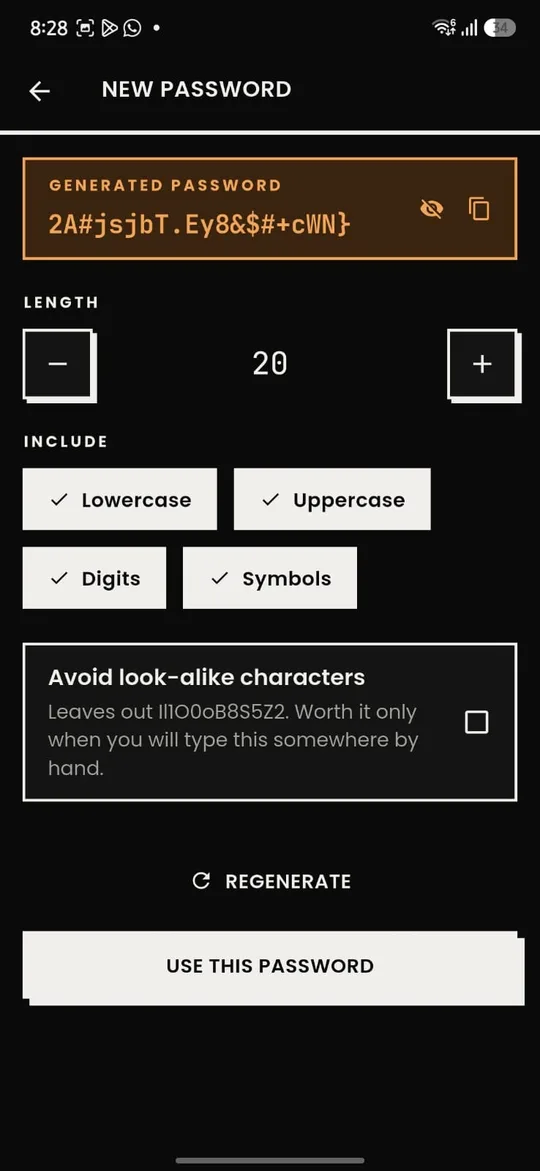
Password generator
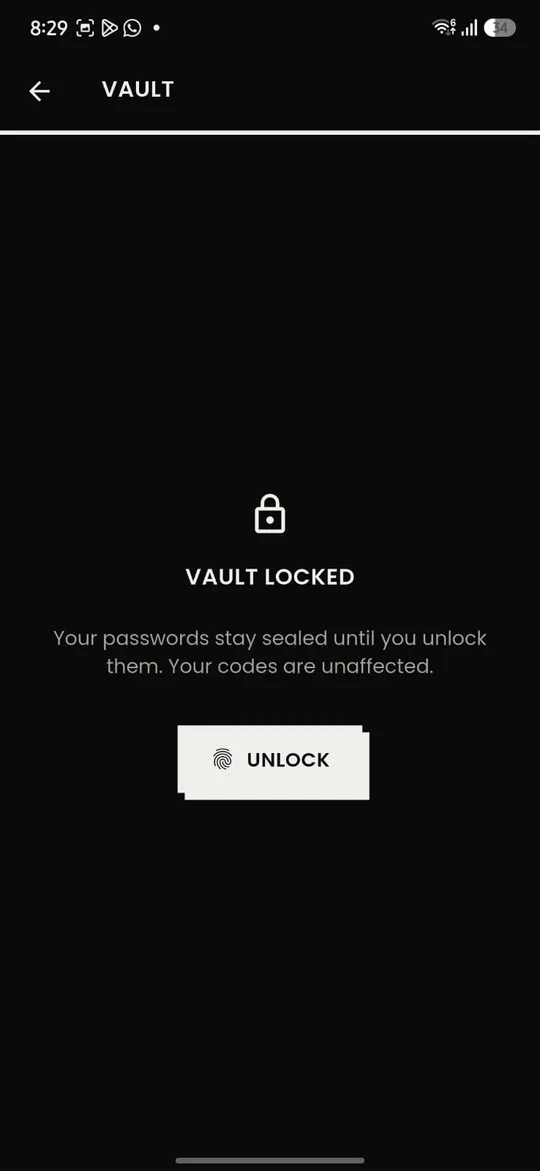
Vault, locked
Problem
An authenticator holds the second key to every account it protects, yet most of them sync to a cloud, fetch account logos and run analytics, and each of those is a path for a secret to leave the phone.
Approach
Remove the network. KyAuth makes no outbound request at all, not even to load a font. Codes follow RFC 6238 and RFC 4226 and are tested against the published vectors; secrets sit in an encrypted database unlocked by a hardware-backed key, behind a biometric app lock with auto-lock and screenshot protection. The interface is monochrome, and the only colour in the app appears when a secret is exposed on screen.
Outcome
The authenticator is feature-complete and verified on an Android device: QR and manual enrolment, live codes, search, drag reorder and app lock. In development is the password vault, so one app holds a login and its second factor together.
Who it is for
People who protect their accounts with two-factor codes and want the app holding those secrets to have no way of sending them anywhere.
Built on
Stack
Flutter · Dart · Riverpod · go_router · Drift · flutter_secure_storage · local_auth
Kyron Infotech designed, built and maintains KyAuth. It is our own software, so the code, the decisions and the mistakes are ours to show you.